Community Platform Data Privacy: Own Your Member Data
Who owns member data on a community platform, which privacy laws apply (GDPR, DPDP, CCPA), SaaS vs self-hosted control, and a practical WordPress setup.
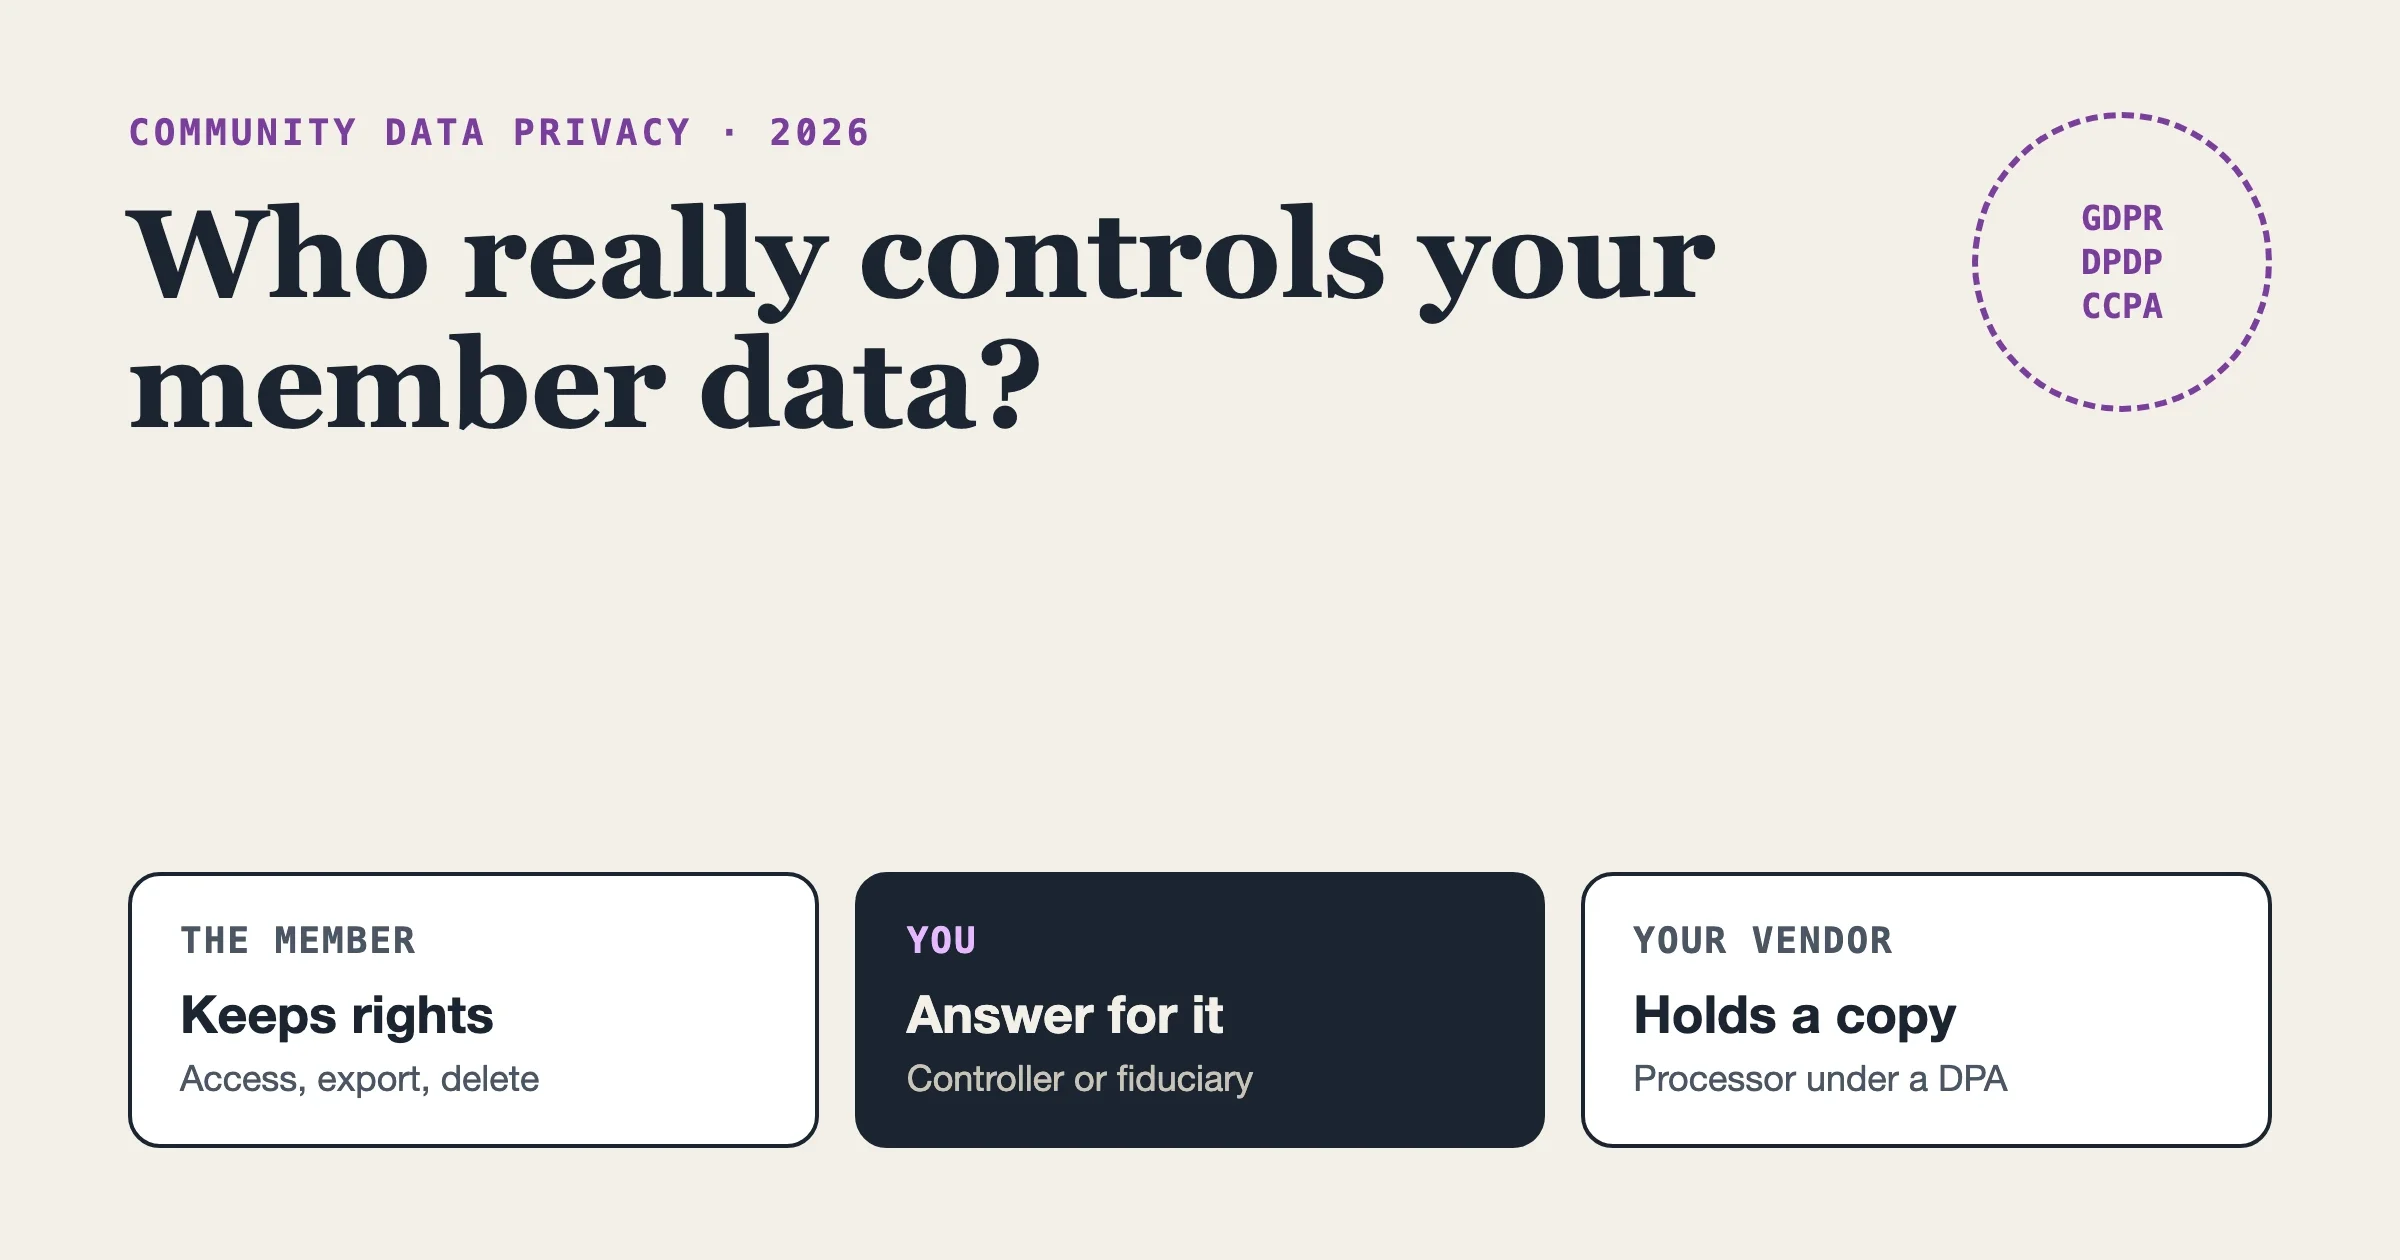
You own your member data in law when you are the “data controller”: the organisation that decides why and how members’ personal data is collected. That is true whether your community runs on your own WordPress site or on a SaaS platform. What changes is your practical control. On a self-hosted platform you hold the database, choose where it lives and can export or delete any record yourself. On SaaS you depend on the vendor’s tools, contract and export options to meet the same duties.
This guide explains what that means for a community in late 2026: which privacy laws usually apply, what members can ask you for, where SaaS and self-hosted platforms differ, and the practical setup we use when we build communities on WordPress. Laws and versions were checked on 21 November 2026. It is general information from a team that builds community sites, not legal advice; for decisions about your own obligations, talk to a privacy lawyer in your market.
Who owns member data on a community platform?
Three parties touch member data, and it helps to name them the way privacy law does.
- The member is the person the data is about (a “data subject” under the EU GDPR, a “data principal” under India’s DPDP Act). They keep rights over it: to see it, correct it, take it with them and, in many cases, have it deleted.
- You, the community owner, are normally the controller (the GDPR term) or data fiduciary (the DPDP term). You decide what is collected and why, and you answer for it.
- Your vendors (a SaaS community platform, your host, your email service, an analytics tool) are usually processors. They handle data on your instructions under a contract. Article 28 of the GDPR requires that contract, which most vendors call a Data Processing Agreement (DPA).
So “owning” your data is less about a legal title and more about control. If the vendor holds the only copy, sets the export format and decides how long backups are kept, your control is only as good as their contract and tools. That is the real trade-off behind every SaaS versus self-hosted decision.
Why is a community more sensitive than an ordinary website?
A blog collects an email address. A shop collects an address and a payment token. A community collects behaviour over time: who talks to whom, which groups someone joins, what they post in private messages, the photos they upload, and often their real name, job and location on a profile. Put together, that is a detailed picture of a person.
Some communities go further and touch special categories of data by their nature: health support groups, faith communities, LGBTQ+ spaces, recovery groups. Under GDPR Article 9, data revealing health, religious beliefs or sexual orientation needs extra care and a specific legal condition to process. If your community is one of these, privacy is not a feature list item. It is the reason members feel safe enough to post.
Which privacy laws apply to an online community?
Usually more than one. Laws tend to follow the member, not the server, so a small community with members in several countries can fall under several regimes at once. Here are the ones we see most often in client projects.
Law | Who it covers | Key duties for a community | Penalty ceiling |
|---|---|---|---|
EU GDPR (in force since 25 May 2018) | Organisations in the EU, and those outside it that offer services to people in the EU or monitor their behaviour (Article 3) | Lawful basis, privacy notice, access, erasure and portability rights, breach notice to the regulator within 72 hours where feasible, DPA with processors | Up to EUR 20 million or 4% of worldwide annual turnover, whichever is higher (Article 83) |
India DPDP Act 2023 and DPDP Rules 2025 (Rules notified 14 November 2025) | Processing of digital personal data in India, and outside India when offering goods or services to people in India | Consent notice per purpose, respond to rights requests within 90 days, inform affected people of a breach without delay, parental consent for children | Up to INR 250 crore for failing to keep reasonable security safeguards; up to INR 200 crore for breach-notice or children’s data failures |
California CCPA as amended by the CPRA | For-profit businesses that meet set revenue or data-volume thresholds and handle California residents’ data | Notice at collection, right to know, delete and correct, opt-out of sale or sharing | Civil penalties per violation, enforced by the state |
Sources: the GDPR text on EUR-Lex, the Government of India PIB note on the DPDP Rules, 17 November 2025 and the California Attorney General CCPA page. Brazil’s LGPD, Canada’s PIPEDA and a growing list of US state laws follow similar patterns. If you have members in a country not listed, check its law; do not assume one framework covers everyone.
Does GDPR apply to my community if I am not in the EU?
It can. Article 3(2) of the GDPR extends it to organisations outside the EU that offer goods or services to people in the EU, or monitor their behaviour there. A community that welcomes EU members, takes payments in euros or tracks member activity across the site will usually be in scope. One stray EU visitor to a purely local community is a different case, which is why “it depends” is the honest answer and why a lawyer’s view is worth having for a paid community.
If GDPR applies, the duties that matter most in day-to-day community work are these:
- A lawful basis for each use of data. Running the community you promised members is usually “contract”; marketing emails usually need consent.
- Answering rights requests within one month, extendable by two further months for complex requests (Article 12).
- Erasure and portability. Members can ask you to delete their data (Article 17) and to receive it in a machine-readable format (Article 20).
- Breach notification. Tell the supervisory authority within 72 hours of becoming aware of a breach, where feasible, unless it is unlikely to put people at risk (Article 33), and tell members when the risk is high (Article 34).
- Children. Where consent is the basis for an online service offered to a child, the default age is 16, and member states may lower it to as young as 13 (Article 8).
What does India’s DPDP Act require from community platforms?
India’s Digital Personal Data Protection Act was passed in August 2023, and the DPDP Rules that make it work were notified on 14 November 2025, according to the government’s own summary. The Rules give organisations an eighteen-month window for phased compliance, so most duties bite from around May 2027. If you have members in India, use that window now; rebuilding consent and deletion flows takes longer than it looks.
Points that matter for a community:
- A separate, plain consent notice explaining the specific purpose for collecting data.
- Rights requests for access, correction, updating and erasure must be handled within a maximum of ninety days.
- Breaches must be reported to affected people without delay, in plain language, with what happened and what they can do.
- Children’s data needs verifiable consent from a parent or guardian.
- A visible contact for privacy questions, which may be a designated officer or a Data Protection Officer.
Larger platforms can be classed as Significant Data Fiduciaries, with independent audits, impact assessments and, in some cases, government directions on keeping certain data in India. Most independent communities will not reach that level, but a fast-growing network should watch for it.
What do SaaS community platforms control that you do not?
SaaS platforms such as Circle, Mighty Networks, Hivebrite, Bettermode, Skool and Discord are quick to start, and for many groups that speed is the right call. The privacy questions are about control, and they are worth asking before you sign up, not during a migration.
- Where data is stored. Many US-based platforms host in the US. Transfers from the EU are lawful under the EU-US Data Privacy Framework (adopted by the European Commission on 10 July 2023) if the vendor is certified, or under standard contractual clauses. Check which one your vendor relies on.
- What the export includes. Read the vendor’s export documentation and test it. Member lists and posts are commonly exportable; private messages, reactions, group history and uploaded files often are not, or arrive in a format no other tool can import.
- How fast you can answer a member. If a member asks for all their data, you have one month under GDPR and up to ninety days under DPDP. If the vendor’s tools cannot produce it, the deadline is still yours.
- What happens to data when you leave. The DPA should say how long the vendor keeps data and backups after you cancel and how deletion is confirmed.
- Price and policy changes. When Ning ended its free networks in 2010, many community owners had to pay or move at short notice. The lesson holds: if a vendor changes terms, your community data moves on their timeline.
Regulators also act against platforms directly. In November 2022 the French regulator CNIL fined Discord EUR 800,000 for GDPR failures including data retention and security (decision of 10 November 2022, listed in the CMS GDPR Enforcement Tracker). Owners of communities on that platform had no say in those practices.
SaaS vs self-hosted: how do they compare on data ownership?
Question | SaaS community platform | Self-hosted (for example WordPress) |
|---|---|---|
Who holds the database? | The vendor | You (or your host, under your account) |
Where is data stored? | Where the vendor hosts; sometimes a region choice on higher plans | Wherever you choose a server |
Full export of members, posts, messages, files | Depends on the vendor’s export tools | Yes: database dump plus the uploads folder |
Verified deletion of one member | Through vendor tools; backups follow vendor policy | You can confirm it in the database; you also own backup retention |
Security patching | Done by the vendor | Your job (or your maintenance provider’s) |
Breach detection and notice | Vendor tells you; you notify regulators and members | You detect, assess and notify |
Running cost | Monthly fee, often per member or per tier | Hosting, plugins, maintenance time |
Self-hosting gives you control, and control cuts both ways. You get the database and the choice of jurisdiction. You also get the patching, the backups, the monitoring and the breach response. If nobody on your team will own those jobs, a well-run SaaS vendor may protect members better than an unmaintained self-hosted site.
Does self-hosting on WordPress make you compliant?
No. It gives you the tools to comply, which is different. WordPress core has had two privacy tools since version 4.9.6 (May 2018): Export Personal Data and Erase Personal Data, under Tools in the admin. A member’s request is confirmed by email, then you generate a ZIP export or run the erasure.
The catch is in the WordPress documentation itself: these tools only gather data from WordPress and from plugins that register with them, so you may need to go further to answer a request completely. Each plugin that stores personal data has to register an exporter and an eraser.
Checked on GitHub on 21 November 2026, BuddyPress registers exporters for its activity, profile fields, friends, groups, messages, notifications and settings components, so they appear in the core export. We did not find erasers registered for the core erase tool; BuddyPress removes a member’s community data when the account itself is deleted. In practice that means an erasure request on a BuddyPress site is usually handled by deleting the account, not by the Erase Personal Data screen. Test both on a staging copy before you promise members anything.
How do you register your own data with the WordPress export tool?
If you store member data in custom tables or user meta (a custom profile field plugin, a points system, a form), register an exporter so it appears in the member’s ZIP. This is the documented personal data exporter API. Example below; it reads one user meta key, and you would repeat the pattern for each data store. Checked against the WordPress developer docs and syntax-checked with PHP 8.5 on 21 November 2026.
<?php
/**
 * Add a custom "community_city" profile value to WordPress
 * personal data exports (Tools > Export Personal Data).
 */
add_filter( 'wp_privacy_personal_data_exporters', function ( $exporters ) {
	$exporters['my-community-city'] = array(
		'exporter_friendly_name' => __( 'Community profile extras', 'my-community' ),
		'callback'               => 'my_community_export_city',
	);
	return $exporters;
} );

function my_community_export_city( $email_address, $page = 1 ) {
	$user = get_user_by( 'email', $email_address );
	$data = array();

	if ( $user ) {
		$city = get_user_meta( $user->ID, 'community_city', true );
		if ( '' !== $city ) {
			$data[] = array(
				'group_id'    => 'community-extras',
				'group_label' => __( 'Community profile extras', 'my-community' ),
				'item_id'     => 'community-city-' . $user->ID,
				'data'        => array(
					array(
						'name'  => __( 'City', 'my-community' ),
						'value' => $city,
					),
				),
			);
		}
	}

	return array(
		'data' => $data,
		'done' => true,
	);
}
The matching eraser uses the wp_privacy_personal_data_erasers filter and returns how many items were removed or retained. Put this code in a small site plugin, not in a theme, so it survives theme changes.
What does a privacy-first community setup look like in practice?
This is the checklist our team works through on community builds. It is not exhaustive, and it does not replace legal advice, but it covers the gaps we find most often.
- Map the data. List every place personal data lives: user table, profile fields, activity, messages, uploads, form entries, email service, analytics, backups. For each one note the purpose, who can see it and how long you keep it.
- Collect less. Every required profile field is data you must protect, export and delete. Make fields optional unless the community truly needs them.
- Give members control on the front end. Profile field visibility, a way to leave groups, a way to delete their own posts and a clear “delete my account” route that does not need a support ticket.
- Wire up export and erasure. Confirm every plugin that stores personal data appears in Tools > Export Personal Data, and that account deletion removes community data. Test with a dummy member.
- Respect consent for trackers. Analytics, embeds and anti-spam scripts often set cookies; load them only after consent where the law requires it, and test while logged out.
- Patch on a schedule. Self-hosted means you own updates. Watch the advisories for every plugin you run.
- Plan the breach response. Who decides, who tells the regulator within 72 hours (GDPR), who writes to members, and where the template lives.
- Set backup retention. Deleted members live on in old backups. Keep backups for a defined period and make sure a restore does not quietly bring erased accounts back.
Our post on adding privacy features to a BuddyPress site goes deeper on the member-facing controls.
What does “patch on a schedule” look like for BuddyPress right now?
A live example of why self-hosting needs an owner. Patchstack lists CVE-2026-1360, an authenticated PHP object injection in BuddyPress’s extended profiles component, rated CVSS 8.8 and exploitable by any logged-in subscriber. Patchstack’s entry, published 3 August 2026, marks BuddyPress up to and including 14.5.6 as affected with no official patch available when we checked on 21 November 2026. The CVE.org record (published 30 July 2026) lists versions up to 14.5.0. The sources disagree on the affected range, so do not assume the latest release, BuddyPress 14.5.6 (17 November 2026), closes it.
If you run BuddyPress, keep it updated, limit who can register while the advisory is open, consider a virtual patch from a security service, and review the extended profiles setup. Our honest look at BuddyPress in 2026 covers the wider picture.
Common mistakes people report
These come up repeatedly in public WordPress support forums for consent and privacy plugins. Paraphrased, linked and checked on 21 November 2026.
- Analytics cookies set before consent. A site owner using Complianz with Site Kit found Google Analytics 4 cookies being set before visitors had agreed (Complianz support, November 2026). Install a consent tool, then verify in the browser that nothing loads early.
- Anti-spam scripts loading before consent. Another owner found Google reCAPTCHA v3 loading on a contact page before consent, despite the consent plugin’s integration being switched on (Complianz support, November 2026). Registration and login forms on a community often carry the same scripts.
- Cookies left behind after a member withdraws consent. A user of GDPR Cookie Compliance found Google Analytics and Ads cookies were not removed when consent was revoked; the plugin team pointed to a different cookie removal setting (GDPR Cookie Compliance support, 2026).
- A consent banner that never appears. A Complianz user had the banner enabled for every page, yet visitors never saw it, even in private windows and on mobile (Complianz support, November 2026). Caching and theme conflicts are the usual suspects; check as a logged-out visitor.
- Assuming the core erase tool removes everything. The WordPress documentation warns that the tool only covers WordPress and participating plugins, and that erasure requests should be respected when you restore from backups. Plugins without erasers, and old backups, are where deleted members tend to survive.
Where does BuddyNext fit for owners who want to keep their data?
BuddyNext, from our team, is a self-hosted community platform for WordPress: feed, profiles, groups, messages, forums and more in one plugin, with the data in your own WordPress database. It is free to start, with a paid Pro version. For data ownership that means the same thing as any self-hosted option: you choose the host and region, you can export everything, and you control deletion.
The honest limits: it is a newer product, so there are fewer third-party add-ons and community answers than for BuddyPress, and self-hosting it means your team (or a maintenance partner) owns updates, backups and security. If you already run BuddyPress, our BuddyX and Reign themes support it, and moving later is possible but is a real project. For budget planning, see our breakdown of community website costs.
Frequently asked questions
Do I own my community’s data on a SaaS platform?
Legally you are usually the controller and keep responsibility for it. Practically, the vendor holds the database, so your control depends on their contract, export tools and deletion policy. Read the DPA and test the export before you need it.
Is a self-hosted community automatically GDPR compliant?
No. Self-hosting gives you the access needed to comply, but you still need a lawful basis, a privacy notice, working export and deletion, consent for trackers, security patching and a breach plan.
How long do I have to answer a member’s data request?
Under GDPR, one month, extendable by two further months for complex requests. Under India’s DPDP Rules, a maximum of ninety days. Other laws differ.
Do I need to tell members about a data breach?
Often, yes. GDPR requires notice to the regulator within 72 hours where feasible and to affected people when the risk to them is high. India’s DPDP Rules require affected people to be told without delay. Prepare templates in advance.
Can members delete their own BuddyPress account?
BuddyPress has a setting that lets members delete their own account from their profile settings. Check it is enabled if you want self-service deletion, and test what it removes on a staging site.
Should I host my community in the EU or India for compliance?
Not necessarily. Neither GDPR nor the DPDP Act requires local hosting for most communities; GDPR allows transfers with safeguards, and DPDP allows them except to countries the government restricts. Choosing a region can still simplify contracts and reassure members.
The short version
You are responsible for member data wherever it lives. SaaS gives you speed and hands much of the control to the vendor. Self-hosting gives you the database and the jurisdiction, along with the patching and breach response. Pick the model your team can actually run well, map the data, test export and deletion, and get proper legal advice for your markets. If you want help building or auditing a self-hosted community, our team does this work every week; you can start with BuddyNext or talk to us about a BuddyPress build.